Hire by Technology
SERVICES


Most legacy banking systems cannot keep pace with what the market now expects of them. We often work inside lender codebases, only to find that critical operations are still running on infrastructure built decades ago.
While patching this software together year after year can seem cheaper up front, it eventually means you are getting something incredibly complex and poorly documented.
In these cases, even small integrations swallow months, costing far more than you might have budgeted.
On top of this added complexity, digital-first competitors ship lending platforms in weeks, which means that legacy software is at an even greater disadvantage when it comes to revenue.
And regulators like the OCC, FCA, and EBA can all revise guidance faster than a legacy integration cycle runs, which turns slow architecture into an operational risk as much as a competitive one.
The solution to all of this is API-first banking, which offers lenders a way out of that trap.
Every function gets designed as a callable service from day one, including things like customer onboarding, credit scoring, KYC verification, loan disbursement, and AML monitoring.
Since nothing gets bolted on afterward, later work then costs a fraction of what it would otherwise.
Let’s take a look at everything you need to know about API-first banking as an institution with legacy code, or a fintech startup trying to set yourself up for long-term success.
Our senior fintech developers have worked in both of these situations and can draw on their production experience to benefit you.
An API-first approach treats every function of a banking or lending system as something reachable through an application programming interface. Since they are so critical, this usually means that the APIs become the blueprint for how everything else gets built.
The result is that integration work gets much cheaper when onboarding, KYC validation, and disbursement already exist as modular services.
You skip the middleware layer you would otherwise design and then maintain for years, and also skip the one-off connectors that need rewriting every time something shifts upstream.
All of your different services talk through stable, documented interfaces, so adding something new just turns into routine work.
That’s essentially the direct opposite of older banking integrations, where interoperability was rare, and APIs got grafted onto monolithic cores once those cores already existed. This system means that even small changes could break something downstream.
The numbers suggest this shift has moved well past experimentation. In McKinsey survey work with banking IT executives, 88% of respondents back in 2023 said APIs had grown more important over the previous two years, and large banks reported putting roughly 14% of their IT budget into API work.
APIs give lending systems a reliable way to move data in both directions. There are a couple of really good examples of what that looks like day-to-day.
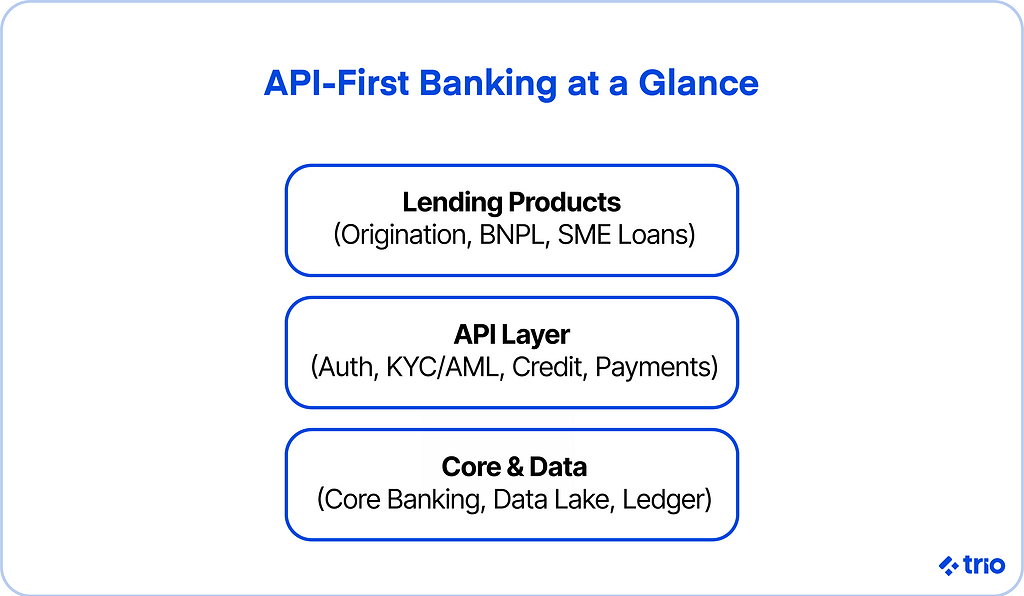
For lending to work, it needs a web of systems to work together, including core banking software, CRM tools, credit bureaus, payment processors, and compliance platforms.
Keeping all of these in sync without APIs means batch file transfers and manual uploads, which produce a massive error rate.
Under an API-first model, on the other hand, data moves in real time, so a submitted application travels from the CRM to the core system, triggers a bureau credit check, and lands in a risk model without anyone touching it.
As this happens, each step leaves a log entry behind. For lenders carrying AML obligations or heading into an audit, that is incredibly useful.
Origination eats a lot of resources through its data validation, eligibility checks, underwriting models, and regulatory review, all of which require real-time data movement.
Batch-based systems struggle to provide everything origination needs, but when origination runs through APIs, systems can validate details, update a risk profile, and fire an approval the moment conditions clear. This means borrowers can get answers much faster.
And again, the decision trail comes along with it, built with less human handling and correspondingly less room for bias to creep in.
Underwriters can almost instantly see a current picture of the borrower instead of an outdated credit report.
To do this, APIs pull from several sources at once, including credit bureaus, open banking feeds, transaction histories, utility payment records, and even payroll data.
In industries with very thin margins, like BNPL and SME credit, this rapid access to accurate information can make a massive difference.
GDPR and its equivalents put a limit on this, though.
Data minimization requirements mean you need a reason for every source you pull, documented and defensible.
Auditing gets easier under an API-first approach, since each source arrives as its own integration with its own access controls, and provenance stays traceable.
We have already alluded to many of the reasons why you may want to use API-first banking, but the primary reasons we see companies swap are faster launches, lower operating costs, better customer experience, and easier scaling.
API-first banking can be used in almost every part of the lending process to automate it. Here are the steps that our developers often help clients take, in order.
APIs can help you pull data straight from web, mobile, and embedded channels into CRM and decisioning systems, which removes issues like duplicate entry entirely and ensures applications arrive clean and consistent.
We usually see schema validation at this layer to repay the effort quickly. A contract that checks required fields, formats, and types at the door stops bad data before it reaches a credit decision or trips a compliance flag.
Through extensive automation, checks that used to take days finish in seconds.
Connecting to credit bureaus and identity verification providers is probably the first step to take here, since it returns structured KYC and AML results straight into your decision models.
Sanctions screening belongs at this layer as well.
Whether you call OFAC, the UN consolidated list, or a commercial provider, an API-first setup lets the check run synchronously inside the application flow, so no approval goes out before screening comes back.
In some cases, funds can now even reach the borrower without a person touching data anywhere along the way, with approval automatically triggering transfer or contract generation.
We’re seeing an interesting shift here, with where human review fits becoming the interesting design question.
There are plenty of loans that should never auto-approve, and regulated lenders generally need configurable review queues for the edge cases.
You set the thresholds, the APIs hold them, and review fires only where it earns the delay.
A major use case we help implement is portfolio visibility, which can be forced to current. Automated notifications also mean borrowers hear from you on time.
APIs connect repayment tracking and reminders to your communication and accounting platforms, feeding dashboards as they go. Regulatory reporting fits here for most lenders.
Call reporting, HMDA data, and state-level obligations can draw directly from API transaction logs, which already hold the structured data those filings want. A manual data pull becomes a scheduled call against an endpoint you already built.
Unfortunately, migrating to an API-first approach can present its own difficulties.
One of the best examples of API-first banking used by lenders is in BNPL and embedded credit. It is also an example that many users are familiar with.
All customers see is a two-click approval, but there is a fair amount that happens underneath.
Identity verification, soft credit checks, fraud detection, and risk scoring all run through APIs in the gap between tapping a payment option and seeing a decision. This means that every step needs to happen incredibly quickly.
Latency sets a hard ceiling on the design, since checkout conversion falls off as approval time climbs.
Chaining synchronous calls one after another is just not an option, so developers usually implement parallel calls with merge logic, along with risk signals computed earlier in the session and cached for the moment they are needed.
Models that learn from each cycle suit short-duration credit better than traditional scorecards. APIs can help you feed them real-time behavioral and transactional data, like purchase history, repayment timing, and whatever else the lender has consent to use.
As we’ve seen the technology develop, it’s become clear that affordability has become the regulatory pressure point.
UK firms came under FCA regulation on 15 July 2026 and must check that borrowers can afford to repay.
Australia folded BNPL into the National Credit Act through its low-cost credit contract reforms, with modified responsible lending obligations attached.
The US went the other way: the CFPB revoked its BNPL interpretive rule in 2025 and has said no replacement is coming.
Where the obligation does apply, open banking APIs offer the most scalable route to meeting it, since a live transaction feed produces the affordability signal without asking anyone to upload bank statements by hand.
Based on what we are seeing right now, it looks like subscription and credit-as-a-service models are going to be where this heads next, with the credit relationship running continuously instead of resetting at each transaction.
Models trained on live API data can read borrower behavior and adjust pricing as conditions move. Pairing structured APIs with ML pipelines produces lending systems that sharpen over time. Explainability sets the limit on how far this can go.
However, this immediately creates concerns around black-box models. You need to be able to explain the decisions made by the AI model at any moment.
The EU AI Act classifies creditworthiness assessment as high-risk with its own transparency obligations attached. SHAP and LIME give teams a workable way to produce human-readable explanations.
API-first architecture helps here as well, since each model call exists as a discrete event with logged inputs and outputs. Teams running batch models over a data lake often find that reconstructing a specific decision after the fact ranges from painful to impossible.
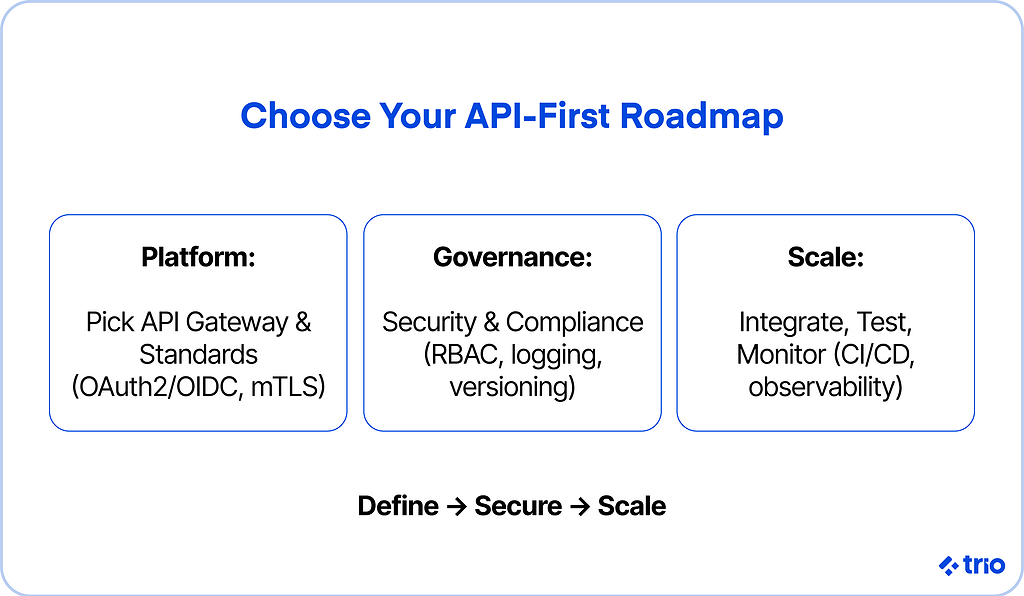
Architecture should follow strategy. You need to understand that a platform built for partnerships looks very different from one built primarily to keep regulatory risk low, so the business goal needs to be set first.
We find it very useful to write the integration contract you would want a credit bureau or open banking provider to hand you, then hold your own APIs to that standard. Working backwards from what a downstream system needs to call can help you create cleaner designs.
Tooling also matters less a lot, but not as much as where you put it.
Apigee, Kong, and AWS API Gateway each bring different strengths, and your existing infrastructure will narrow the field faster than any feature comparison.
Think about your placement in relation to compliance and security controls.
For example, your gateway enforces authentication, rate limiting, and logging, so it has to sit where it can observe everything.
Above all, compliance belongs in the design phase. Retrofitting security and compliance into a published API layer costs a lot more than building them in, which means you need to start thinking about these in design reviews.
Finally, keep in mind that your APIs will need ongoing attention once they ship. Version deprecation, performance monitoring, and security scanning all reward automation.
Penetration testing should run on a schedule rather than in response to incidents, and PCI DSS requires annual testing of the cardholder data environment regardless, which includes any API endpoint touching payment data.
API-first banking is changing how financial systems get built and maintained. Through them, established lenders carrying legacy constraints can move forward without a full rebuild, and newer products reach the market sooner and stay adaptable as the user base grows.
At Trio, our engineers work inside fintech codebases daily, on API layers, compliance integrations, and lending platform architecture.
If you are weighing whether to build an API-first lending system, extend one you already have, or bring in domain expertise to get the security and compliance design right early, we can connect you with engineers who have done this work before, usually within a few days.
Get in touch to learn more about how Trio's fintech engineering talent works.