

 Read Client Stories




 Alex Kugell
 Key Takeaways
- SEPA Instant inbound from January 9, 2025; outbound from October 9. Fedwire completed its ISO 20022 migration on July 14, 2025. SWIFT ended MT/ISO 20022 coexistence for cross-border payments on November 22, 2025.
- On August 27, 2026, SWIFT deferred the payment changes in Standards Release 2026, including the structured-address requirement and the mandatory camt.110 reception date.
- By November 2027, camt.110/111 (investigations) and camt.056/029 (payment cancellations) become the only permitted formats for exceptions and investigations, and in-flow translation to the legacy MT199 format ends.
- ISO 20022 carries structured data fields that enable automated reconciliation, real-time fraud screening, and interoperability across SEPA, SWIFT, Fedwire, RTP, and FedNow.
A year ago, regulators in Europe tightened the screws with SEPA Instant requirements while the world’s largest payment rails transitioned to ISO 20022, a new global standard for electronic financial messaging.
Those deadlines have now passed, but there is still a lot that’s actually still open. Knowing what’s going on can help ensure that you don’t get caught out by the next wave, some of which just moved.
A lot of the original deadlines fell close together, with SEPA Instant required inbound support from January 9, 2025. Fedwire’s message format shifted to ISO 20022 on July 14 of the same year, and SEPA mandated outbound instant payments from October 9.
On top of all of that, on November 22, 2025, SWIFT formally ended the coexistence period between MT and ISO 20022 messages for cross-border payments.
Now, however, the deadline set for November 2026 has been pushed back. SWIFT confirmed on August 27, 2026, that it is deferring the payments-related changes in its 2026 Standards.
If you weren’t ready, this shift buys your fintech some time, but a big mistake right now would be to think the work is no longer needed.
Let’s walk through what already happened, what just moved, and the practical steps you can take now, not just to stay compliant, but to build a payments stack that sets you apart once the dust settles.
For help ensuring your products can utilize the latest payment rails, you are in the right place.
What Already Happened: The 2025 Deadlines
2025 had a lot of changes, making it a rather unusual year. We watched some companies rush to meet the requirements, which meant that they ended up with tech debt and related issues.
January 2025: SEPA Instant Inbound Enforcement
From January 9, payment service providers in the eurozone needed the ability to receive SEPA Instant Credit Transfers.
Even if your fintech doesn’t classify as a bank, if your partner institution touches Europe at any point, you need the ability to process inbound instant payments.
Some providers outside the eurozone, like some EMIs and PIs, had slightly later timelines, but in the euro area, PSPs have been on the clock since January 2025.
July 2025: Fedwire Migrates to ISO 20022
The U.S. Federal Reserve held to its date of July 14 as the migration date for the Fedwire Funds Service. All Fedwire messages now use ISO 20022, and the legacy FAIM format no longer receives support.
October 2025: SEPA Instant Outbound Enforcement
By October 9, eurozone PSPs needed to send SEPA Instant payments.
For a lot of the companies we worked with at the time, this requirement carried more weight than inbound, since outbound flows require changes to customer-facing systems, fraud controls, and reconciliation engines.
There are still a limited number of exceptions for non-eurozone PSPs, but most companies were held to this deadline.
Related Reading: How to Hit Roadmap Deadlines Without Hiring
November 2025: SWIFT Cross-Border Cutover
On November 22, 2025, SWIFT officially ended the coexistence period between MT and ISO 20022 messages for cross-border payments and reporting.
There is still a conversion service to handle remaining MT instructions during the wind-down period, but ISO 20022 is the required format for payment instructions across the SWIFT network, making it a baseline requirement if your fintech is operating globally.
What’s Next: The Deferred 2026 Deadline and the 2027 Deadline That Didn’t Move
Two milestones were originally set for November 14, 2026. There was a requirement to use structured or hybrid postal addresses instead of free-text ones, and a requirement for every institution to be able to receive investigation messages in the new camt.110 format.
On August 27, 2026, SWIFT deferred both of these deadlines, after readiness data showed roughly 61% of payments were still carrying unstructured addresses in April, and after large community banks and domestic payment infrastructures requested more time.
We haven’t seen a revised timetable yet, but expect it by December 2026 at the latest. Realistically, we can expect the deferred items to land in a partial release in the first quarter of 2027.
One thing didn’t move, though.
By November 2027, SWIFT’s Exceptions and Investigations (E&I) migration reaches its hard deadline. This means that camt.110 and camt.111 will become the only permitted formats for investigation requests and responses, camt.056 and camt.029 will become the only permitted formats for payment cancellations, and in-flow translation to the legacy MT199 format ends.
If your fintech touches cross-border payments through correspondent banking relationships, this is the deadline to plan around now.
It’s also important to keep in mind that the delay isn’t uniform.
The Bank of England, for example, is deferring its own November 2026 release in full, but the Eurosystem is exploring whether to proceed with parts of its release while postponing the address requirement, and SEPA’s scheme management board was still deciding its position as of early September 2026.
ISO 20022 Exception Handling: From Free-Text MT199 to Structured Case Management
Under the legacy process, when a cross-border payment gets stuck, no reference matches, a sanctions review holds it, remittance data goes missing, the bank investigating it sends a free-text MT199 message to the next bank in the chain. That bank passes it along, and the response works its way back the same way.
SWIFT estimates that more than 70% of exceptions and investigations messages are still unstructured free text, that the average case takes 5 to 10 manual interventions, and that the industry loses roughly $1.6 billion a year in operational costs to this process.
Case Management, which is set to replace SWIFT, uses two pairs of structured ISO 20022 messages instead:
camt.110 and camt.111. are used for raising and resolving an investigation, and camt.056 and camt.029 for stopping or recalling a payment that’s still in flight.
Every field (purpose, remittance details, and regulatory reason) is structured and machine-readable rather than buried in free text, and SWIFT cites resolution-time reductions of up to 80% once a case runs through Case Management instead of the legacy MT199 chain.
For fintechs, this connects directly to reconciliation. The same exceptions that a payment reconciliation system flags internally (missing bank credits, unknown transactions, and disputes) are often the ones that end up as E&I cases with your banking partners.
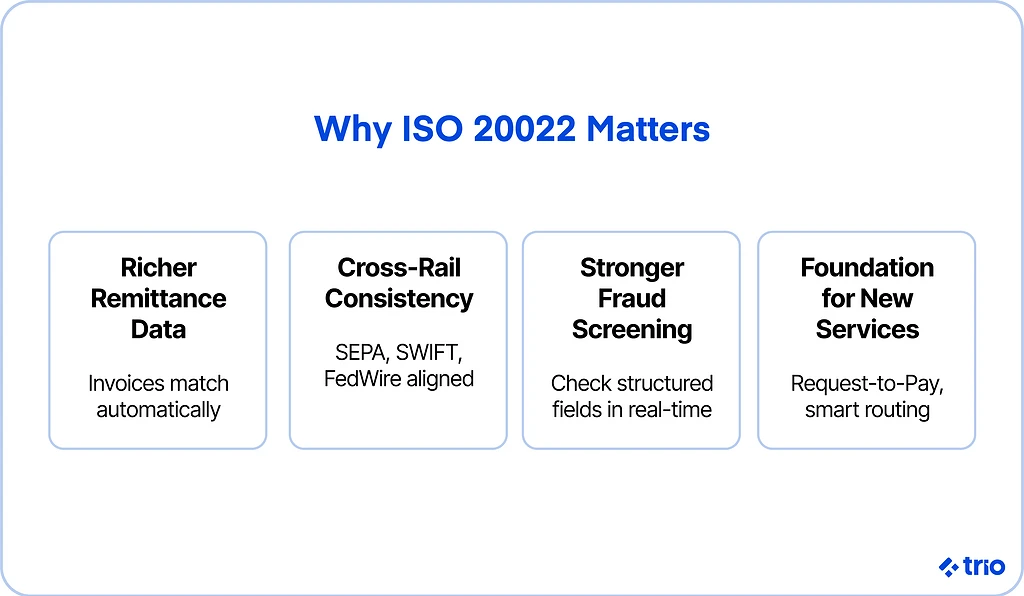
Why ISO 20022 Matters
ISO 20022 marks the establishment of a shared language for payment rails that has the ability to carry meaning rather than bare-bones instructions.
Legacy formats have previously left banks and fintechs only able to pass around information like amount, account, reference, and little else. This created difficulties in dealing with the many errors that occurred, and made fraud detection a lot slower.
ISO 20022 changes the equation by embedding structured, data-rich fields into every message. The G20 and the Committee on Payments and Market Infrastructures (CPMI) have both endorsed the standard, which represents one of the first genuine attempts at an end-to-end global payments grammar.
What That Unlocks in Practice
- Automated reconciliation: invoices match payments without manual intervention because the remittance data actually lives in the message.
- A common structure across SEPA, SWIFT, Fedwire, RTP, and FedNow, which removes the need for a separate mapping engine per network.
- Stronger fraud screening: structured fields let you check KYC data, sanctions flags, and behavioral patterns in real time rather than parsing unstructured text.
- Higher straight-through processing rates, cutting the manual steps that add cost and introduce errors.
- A foundation for overlay services, including Request-to-Pay, dynamic payment scheduling, and financing offers that depend on clean, complete transaction data.
While the upfront infrastructure implications can be costly, you should see it as a strategic investment that becomes the backbone for global reach.
Key Technical Challenges for Fintechs
Most fintech stacks weren’t designed for instant settlement or for messages packed with structured data. That gap tends to show up in a few critical areas.
Coexistence of Legacy and ISO Messages
Rails continue to run both formats simultaneously in places, and the E&I workstream above adds a second coexistence period on top of the 2025 one.
Your systems need to recognize and reconcile messages in both formats in real time, which means orchestration middleware to handle the differences rather than brittle point-to-point fixes that collapse under volume.
The middleware layer buys time without forcing a full rewrite of downstream systems.
Related Reading: Boost Approval Rates with Intelligent Payment Routing
Real-Time Fraud Detection with ISO 20022
Once money settles, recovering it can be virtually impossible, and in the rare cases where you can do something, it may take weeks. That puts pressure on fraud models to operate at millisecond speed.
Fortunately, ISO 20022’s structured fields give AI-powered models considerably more to work with: cleaner KYC data, structured counterparty information, and behavioral signals that were previously buried in unstructured text.
If your team can wire detection logic directly into the transaction path, rather than running it as a downstream check, you will probably catch more without generating excessive false positives. Developers still need to account for global data handling and security standards when deciding where models run and what data they can access.
There are already third-party detection models built specifically for ISO 20022 that can help you reach production faster than building from scratch, and many have already cleared the compliance review process.
Scalability of Infrastructure
“Always-on” shifts from a marketing claim to a hard technical requirement once instant rails are in play, with transactions flowing around the clock and spikes that ignore business hours.
Horizontal scaling and API-first design help, but only deliver results if you’ve load-tested against realistic payment volumes.
Testing and Migration Governance
In the rush to meet the 2025 deadlines, a lot of companies skipped testing and migration governance at the level the industry would usually demand.
We’re also seeing a couple of firms still living with parallel runs and version mismatches as a result.
With a second migration now underway for exceptions and investigations, automated testing and staged environments matter just as much this time.
Teams that build personal accountability into their DevSecOps practices tend to surface issues earlier, which is essential when you consider that fixing them early costs far less than it would mid-migration.
How Fintechs Can Prepare
As we have already mentioned, the firms that come through this change and any others in good shape are the ones who start early and design with both compliance and resilience in mind.
Audit Your Payments Stack
Whether you’re catching up on the 2025 migration or getting ahead of the 2027 E&I deadline, you need to start by mapping every component that touches payments, messaging engines, fraud detection modules, reconciliation tools, and how data flows between them.
You’ll quickly identify where ISO 20022 mapping doesn’t exist yet and where legacy assumptions will break. That map also helps you prioritize, since not every system carries the same level of urgency.
Implement Translation and Orchestration Layers
During the coexistence periods you’ll be living with for a while. This means that you need a way to process both ISO and legacy messages without breaking downstream systems.
Middleware that normalizes message formats provides consistency through the transition, and it helps you avoid the temptation to hardcode patches in multiple places, each of which becomes its own maintenance burden later.
Embed Real-Time Fraud Detection
Traditional fraud checks run in minutes or hours, but that’s too slow by several orders of magnitude when you are dealing with instant payments.
With ISO 20022, the data you need to identify and address high-risk behavior before settlement lives in the message itself.
Engage With Your Providers
If you rely on payment service providers or larger banks, their migration schedule may not align with yours.
We highly recommend that you find out about any gaps before you go live, and confirm directly rather than assuming your provider moved on the same timeline SWIFT originally published.
Strategic Opportunities Beyond Compliance
While it may be a bit of a headache to deal with international changes like this, there are real benefits beyond regulatory compliance.
Cross-Border Reach
Since ISO 20022 aims to become an industry standard, it can connect to multiple markets with less friction.
This means that, instead of maintaining a half-dozen mapping rules, you’re working from a common data language, which makes it easier to scale into new geographies with fewer errors than the previous approach required.
Overlay Services That Customers Notice
Services like Request-to-Pay, dynamic payment scheduling, and financing offers triggered at the point of transfer are already making an appearance in many European markets.
ISO 20022 makes them workable at scale in ways the legacy format couldn’t practically support, thanks to the wealth of information available at any step of the money-moving process.
Analytics-Driven Products
Real-time dashboards for merchants, predictive cash-flow tools for small businesses, and personalized financial insights for consumers all become easier to build when the underlying data actually has structure.
Related Reading: Alternative Data for Credit Underwriting
Resilience as a Differentiator
A lot of the fintechs we work with unfortunately still treat resilience and fraud prevention like overhead that just eats their time and resources, but the reality is that faster settlement times with lower false-positive rates and tighter fraud controls can form a legitimate part of your value proposition.
Customers notice when transfers clear instantly and securely, and as competitors offer these very same services, it starts to set expectations you need to live up to.
Conclusion
We flew past the 2025 deadlines, and the 2026 deadline that was supposed to come next just moved. But none of this means that you can stop preparing.
The November 2027 deadline for exceptions and investigations still looks like it’s going to hold, and the deferred items are probably going to resurface in a couple of months.
Instant rails and ISO 20022 are going to play a big part in global scaling and instant payment settlement, but only if you’re able to move quickly enough to take advantage of new developments.
Our payments experts at Trio can help you figure out where you actually stand.