

 Read Client Stories




 Alex Kugell
 Key Takeaways
- Software change management refers to tracking and managing changes to code, dependencies, documentation, and other artifacts throughout the development lifecycle. In fintech, it also covers audit trails.
- DORA, effective January 17, 2025, requires EU-regulated financial entities and their designated critical ICT providers to run documented ICT change management for critical systems.
- PCI DSS Requirement 6 governs change management controls for systems in the cardholder data environment, where changes must be documented with a description, impact, and risk assessment before deployment.
- Three types of changes require different handling: standard (low-risk, pre-approved, automatable), normal (planned changes needing risk assessment and approval), and emergency (urgent fixes that require rapid response with post-implementation review).
- The most common source of failed changes is an insufficient risk assessment for changes that looked low-risk on paper but weren’t.
Change management plays a critical role in successful software development, and that holds doubly in fintech, where every change to a payment system, a KYC pipeline, or a core banking integration carries compliance consequences alongside the usual engineering risk.
The most effective software developers track changes systematically throughout the development lifecycle.
In fintech, that discipline is further motivated by DORA, which became fully applicable in January 2025, and explicitly requires financial entities to document that changes to critical ICT systems follow a defined, controlled process.
PCI DSS Requirement 6 is similarly specific about what change management controls must look like for systems in the cardholder data environment.
Let’s go over what software change management actually is, how the process works, the three types of changes your team will encounter, and the best practices that matter most in a regulated financial environment.
At Trio, our developers are already familiar with industry regulations and best practices for software change management in fintech.
What Is Software Change Management?
In software development, change management refers to tracking and managing changes to artifacts. This includes code, project requirements, dependencies, documentation, and risk assessments.
A change, in this context, means adding, removing, or modifying any artifact that affects the software development lifecycle.
Three related terms are worth distinguishing:
Change management models refer to the established best practices for managing change within an organization, drawn from frameworks like ITIL and DevOps
Change management processes describe the sequence of steps for moving a change from inception to delivery
Change management plans define the specific roadmap for executing a particular change
Change control is the narrower, approval-focused part of change management: who authorizes a change, on what evidence, and how that authorization is recorded. Auditors tend to use this term rather than change management, and in regulated environments it is the part they test
Release management governs how approved changes are bundled, scheduled, and shipped. Change management decides whether a change should happen; release management decides when and in what package it reaches users
Modern change management functions as a form of risk management that provides transparency and audit evidence throughout the change lifecycle.
For fintech specifically, we often see how those audit trails have direct regulatory value. A well-maintained change log is exactly what a PCI DSS auditor or a DORA supervisory authority will ask to see.
Managing changes in software development typically includes:
Creating a process for identifying and addressing changes, whether bug reports, source code modifications, or dependency updates
Determining how to update the status of a file after a change has been made
Tracing changes back to the original source code and requirements using historical data
Controlling access and administrative rights so that the right people can make changes with appropriate authorization
Documenting the impact of changes on the codebase and the regulated systems it supports
Why Software Change Management Matters
Change management minimizes disruptions and reduces incidents. It speeds up development and leads to better work output, also generating the evidence that compliance reviews require.
Agile development calls for continuous changes. The whole point of iterative development is to respond to feedback throughout the lifecycle, which creates constant change pressure.
Without a structured approach to managing that pressure, changes accumulate without documentation, approvals become informal, and the compliance audit trail disappears.
The consequences of poor change management extend to other issues, too, especially in regulated environments.
Many organizations report downtime costing more than $300,000 per hour. For payment processors or digital banks, that figure can be considerably higher.
A payment system outage caused by an undocumented change that wasn’t rolled back cleanly creates a regulatory disclosure obligation.
On top of all of that, the software change management process delivers faster releases, cross-team collaboration, and real-time visibility.
And, if you are navigating DORA, SOX, or PCI DSS simultaneously, it also delivers the evidence management that compliance frameworks demand.
Types of Changes
Understanding the three types of changes helps teams allocate process overhead appropriately, rather than treating a minor configuration update the same way as a core payment system migration.
Standard Changes
Standard changes are low-risk, commonly repeated, and pre-approved. They happen frequently, follow a documented and approved process, and don’t need to go through a full change advisory board review every time.
Adding memory or storage to a server, replacing a failing hardware component, or creating a new database instance all fall here.
Because these changes have already gone through risk assessment once and the process is well-defined, they represent a prime opportunity for automation.
Some teams report that up to 70% of standard changes can be automated, freeing engineering time for normal and emergency changes that actually require judgment.
In a fintech context, routine configuration updates in non-PCI-scope environments, pre-approved dependency version bumps, and scheduled certificate renewals often qualify as standard changes once the initial assessment is complete.
Normal Changes
Normal changes aren’t emergencies, but they don’t follow a pre-approved process either. They require risk assessment and approval before implementation.
Upgrading to a new content management system, migrating to a different data center, or refactoring a significant portion of the payment processing layer all fall into this category.
These changes need to go through the change management queue: risk assessment, stakeholder review, approval, implementation with documentation, and post-implementation review.
Some normal changes are high-risk and may warrant change advisory board review. Others can move through a lighter approval process with a designated change authority or automated risk scoring.
The key is that the risk level determines the process overhead, not the volume of the change.
Any change touching a cardholder data environment, a KYC pipeline, an AML screening system, or a payment gateway integration should be treated as a normal change at a minimum because PCI DSS Requirement 6 requires documenting the description, impact, and risk assessment for changes to CDE systems before deployment.
Emergency Changes
Emergency changes arise from unexpected failures or threats and need immediate response. Server outages, critical security patch deployments, and major incident resolution all fall here.
The urgency means these changes can’t wait for a full review cycle because the risk of delay usually exceeds the risk of the change itself.
Even so, emergency changes should have a lightweight approval process (not no process), clear post-implementation documentation, and a post-incident review that determines whether the root cause should trigger a normal change to prevent recurrence.
In fintech, emergency changes carry an additional consideration, since you need to consider whether the incident that triggered the emergency change requires regulatory disclosure.
Under DORA, major incidents require a three-stage reporting cadence to the National Competent Authority. The initial report is due within 4 hours of classifying the incident as major, and no later than 24 hours from the moment the entity became aware of it.
The intermediate report follows within 72 hours of that initial report, and the final report within one month of the intermediate one.
Just keep in mind that the clocks run from the previous submission rather than from the incident, which is the detail teams most often get wrong when they build the tracking.
The Software Change Management Process
The change management process varies by organization and framework, but the following sequence applies broadly across both ITIL-aligned and DevOps teams.
1. Change Request
Someone within the organization proposes a change. The request should document the purpose, the expected implementation approach, affected systems, and a preliminary risk assessment.
The key discipline here is that changes should have a stated purpose, like improving the software product or addressing a specific risk, rather than being made informally without documentation.
2. Change Request Review
A change manager or peer reviewer assesses the initial request. Three things are worth checking explicitly rather than by instinct: which dependencies the change touches, whether any related incident is currently open, and whether it collides with scheduled maintenance.
A routine upgrade to a service whose upstream dependency is mid-incident should wait for a word from that service's owner, however low-risk the change looks on its own.
They need to consider things like how likely it is to succeed, whether the risk assessment is accurate, and whether it warrants the process overhead being proposed.
The outcome is not binary either.
A reviewer can narrow the deployment scope, push the change to a quieter window, or let it proceed on condition that a tested rollback is in place.
In a DevOps context, this review can often be automated for low-risk changes or handled through structured peer review rather than a committee meeting. Automation needs a stop condition, though.
An open production incident, unfinished maintenance, or a change touching a critical dependency should drop the request back to a named human for sign-off rather than sailing through on the standard path.
3. Change Plan
The team then creates a game plan covering expected outcomes, resources, timeline, testing requirements, rollback procedures, and the specific systems affected.
For fintech teams, this plan should explicitly name any compliance implications. In other words, consider whether the change touches a PCI DSS-scoped system, an AML-monitored data flow, or any component within DORA scope.
4. Change Approval
The appropriate authority, usually a designated change manager, peer reviewer, or change advisory board, reviews and approves the plan.
ITIL 4 increasingly encourages decentralizing change authority to the business stakeholder or peer level rather than requiring all changes to flow through a central committee, which can become a bottleneck.
Reserve CAB review for the highest-risk changes where broader input genuinely adds value.
5. Change Implementation
Implement the change and document what happens throughout.
Make sure that you monitor for unexpected behavior. In a CI/CD pipeline, this step benefits from automated testing gates that catch regressions before the change reaches production.
If your team is operating under DORA, logging and monitoring during implementation is part of the required evidence-based, not optional, instrumentation added after the fact.
6. Change Closure
Once implementation succeeds, review the outcome. Was the change successful, delivered on time, within budget, and accurately estimated?
Finally, close the change, retain the documentation, and identify whether the experience reveals any improvements to the process itself.
Changes to production financial systems that didn’t go exactly as planned should feed back into risk calibration for future similar changes.
Change Management Best Practices for Fintech
Now that you know a bit about the software change management process, you should look at some best practices to make certain your process is sound.
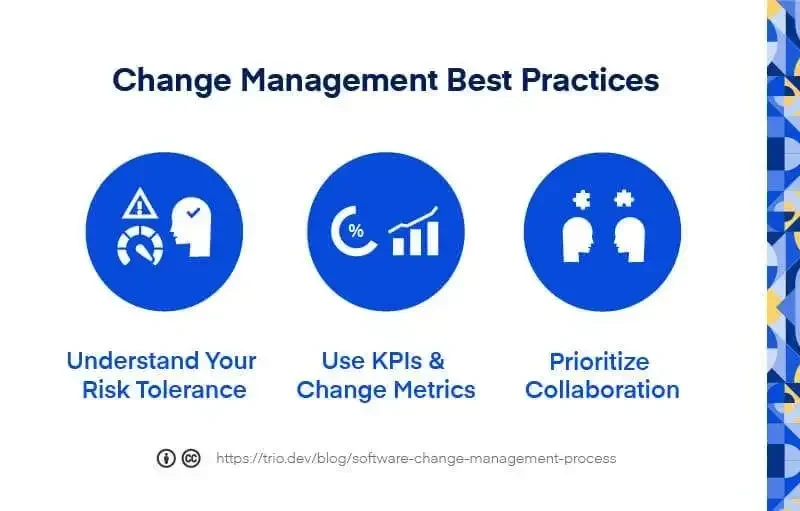
Understand Your Risk Tolerance and Regulatory Obligations
Running a fintech company means managing both engineering risks (what downtime can the system sustain?) and compliance risks (what documentation is required before this change goes live?).
For EU-operating fintechs, DORA’s requirements for documented change management processes apply to critical ICT systems. For fintechs processing card payments, PCI DSS Requirement 6 applies to systems in the CDE.
SOX-impacted fintechs face a similar requirement, since change management documentation is part of the IT general controls that SOX auditors assess.
Teams that treat change management as a compliance overhead rather than a development practice tend to fail those audits more often than teams where change management runs as a natural part of the engineering workflow.
Automate Standard Changes
For most teams, standard changes are going to represent the majority of change volume.
Automating these is a great way to free up engineering time for the normal and emergency changes that actually require judgment.
On top of that, automation also improves compliance. An automated change pipeline generates consistent, timestamped documentation for every standard change, producing exactly the kind of audit-grade evidence that DORA and PCI DSS look for.
A manual process that produces documentation sometimes is less defensible than an automated process that produces it always.
Use KPIs and Change Metrics
Key performance indicators and change metrics are essential for improving the change management process over time.
Useful metrics include:
Change failure rate (the percentage of changes that require rollback or result in incidents).
Mean time to restore after a failed change.
The percentage of changes that followed the defined process versus those that bypassed it.
The ratio of standard to normal changes over time (a growing standard-change percentage typically indicates a maturing process).
Prioritize Collaboration Across Teams
Changes in fintech rarely affect only the engineering team. Instead, the changes can affect compliance (PCI DSS scope), operations (monitoring and incident response), and potentially legal (disclosure obligations if something goes wrong).
Those within your organization need to be forewarned and forearmed with relevant information before a change goes live.
In a DevOps context, this means building change communication into normal workflows that include clear PR descriptions explaining why a change is being made, automated notifications to relevant stakeholders when changes touch specific system components, and post-implementation reviews that include compliance and operations alongside engineering.
Test Failure Deliberately With Chaos Engineering
Chaos engineering, which is the process of deliberately shutting off or degrading components under controlled conditions to observe how the system handles stress, is one of the most effective tools for understanding the actual risk profile of change-related failures before they happen in production.
Resilience engineers test how systems behave under high traffic, high transaction volume, or partial component failure.
Chaos engineering is particularly great in fintech because it surfaces the failure modes that change-related incidents most commonly reveal, like cascading failures when one service goes down, data inconsistencies when a payment write succeeds but the confirmation doesn’t propagate, and recovery procedures that fail under real incident conditions.
Pushing systems to their limits in controlled experiments is considerably cheaper than discovering those limits during a Friday afternoon production incident.
In fact, DORA explicitly requires resilience testing for systemically important institutions, threat-led penetration testing every three years, with annual vulnerability assessments for all critical ICT systems.
Separate the Deploy From the Release
A lot of change risk disappears when shipping code and switching behavior on stop being the same event.
Feature flags let you deploy a change dark, enable it for internal users, then widen the audience. A rollback becomes a config change rather than a redeploy, which matters at two in the morning. The cost is flag debt, so give every flag an owner and a removal date when you create it.
Canary and progressive rollouts do the same thing at the infrastructure layer. Route a small share of traffic to the new version, watch error rate and latency against the old one, and promote or roll back on evidence rather than on nerve.
Segregation of duties is the control auditors look for alongside both. The person who writes a change should not be the only person who approves it into production, and your pipeline should enforce that rather than relying on people remembering. In smaller teams, this usually means a named second approver rather than a committee.
Blameless postmortems close the loop. A change that caused an incident is evidence about the process, not about the engineer, and teams that treat it the other way round quietly learn to make changes without recording them.
Choose the Right Change Management Tooling
Designing and maintaining a software change management process at scale requires tooling that matches the maturity of the team and the regulatory obligations it operates under.
For ITIL-aligned teams managing complex approval workflows, tools like Freshservice, ManageEngine ServiceDesk Plus, and InvGate Service Management provide structured CAB collaboration, automated risk assessment, and audit-grade documentation.
Jira Service Management integrates directly with CI/CD pipelines through its risk assessment engine, making it particularly useful for DevOps teams that want change management built into the delivery pipeline rather than bolted on alongside it.
For fintech teams specifically, the most important selection criterion is whether the tool generates the evidence base that compliance audits require.
At Trio, we provide fintech teams with senior engineers who bring both the development skills and the domain knowledge to operate correctly within structured change management environments.
Developers who have worked in regulated financial systems already understand why change documentation matters and how to produce audit-ready evidence without treating it as extra work on top of engineering.
If you need to scale your engineering team in a way that preserves your compliance posture, request a consult.