

 Read Client Stories




 Alex Kugell
 Key Takeaways
- The fintechs that win build KYC, consent, and reporting into the product from day one rather than bolting them on later.
- MiCA’s transition period ended in July 2026, DORA has applied since January 2025, and the EU AI Act’s high-risk deadline slipped to December 2027. In the US, the GENIUS Act takes effect by January 18, 2027, with rules still in proposal form, and the CFPB’s open banking rule is on hold.
- The US is fragmented (money-transmitter licensing state by state, with more than 40 licenses to go nationwide), the EU is harmonized but broad, and Asia varies widely.
- AML penalties, multi-billion-euro GDPR fines, and collapses like Wirecard and FTX show what skipping oversight costs.
- Requirements usually shift after engineering starts, so configurable rules, audit-ready logging, and flexible staffing hold up better than one-off builds.
Mobile wallets, peer-to-peer lending platforms, and instant payment apps are all examples of financial technologies now part of everyday life.
But with growth, the rules governing financial services aren’t standing still. Every new product has to contend with shifting regulatory requirements, from data privacy laws to identity verification checks.
For leaders, this creates constant friction.
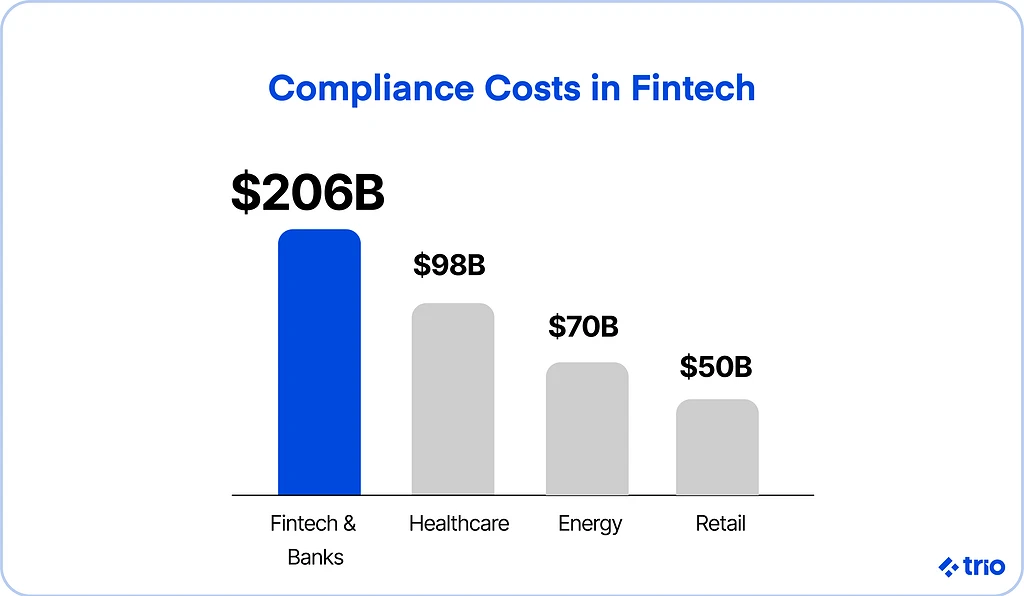
Compliance costs eat into margins, rollout timelines get delayed, and promising ideas sometimes die before reaching the evolving fintech market.
From what we have observed, it seems that the fintechs that win are the ones that treat regulation as a design principle, building compliance into strategy, product design, and customer experience from day one.
Let’s examine how regulatory changes influence innovation, the origins of compliance challenges, and the strategies leaders can employ to maintain their competitive edge.
If you need assistance baking regulatory compliance into your products from the ground up, our fintech-savvy developers are here to help.
Our specialists can also help you comply with a variety of regulatory frameworks and set your products up to account for strategic risk management.
Book a security- and compliance-ready consult.
Fintech Regulatory Changes to Watch in 2026
We’ve watched a lot of changes happen in the last few years, and several changes are to come. Here are some of the main developments recently that you need to be aware of, and what each one means for the people building fintech products.
| Regulation | Region | Status (September 2026) | What it means for engineering |
| GENIUS Act (payment stablecoins) | US | Signed July 18, 2025. Agencies have proposed implementing rules but have not finalized them. Takes effect no later than January 18, 2027. | Issuer-status checks, AML and sanctions controls, and reserve and redemption reporting for issuers. |
| CFPB Section 1033 (open banking) | US | Final rule issued October 2024. A court has blocked enforcement while the CFPB rewrites it, so the original 2026 deadlines are not binding. | Consent management and data-access APIs that can adapt to whatever the final rule requires. |
| Federal Reserve payment accounts (“skinny” master accounts) | US | Proposed May 2026. Comments closed July 27, and the Fed expects to finalize by the end of 2026. | Possible direct settlement for eligible non-banks, with new integration, reconciliation, and reporting work. |
| MiCA | EU | Fully applicable since December 30, 2024. Transitional periods for existing crypto providers ended July 1, 2026. | Authorization checks, AML controls, and EU-specific changes to crypto products. |
| DORA | EU | Applied since January 17, 2025. | ICT risk registers, incident reporting, vendor risk management, and resilience testing. |
| EU AI Act | EU | Transparency duties apply from August 2, 2026. High-risk rules, including credit scoring, now apply from December 2, 2027. | Documentation, human oversight, bias testing, and logging for credit models. |
| PSD3 and Payment Services Regulation | EU | Agreed, with final texts published in April 2026. Formal adoption is pending, and most rules are expected to apply in late 2027 to 2028. | Open banking API performance, strong customer authentication, fraud monitoring, and payee-name verification. |
Notice how many of these rules are still moving. That uncertainty is the real engineering challenge, and we come back to it below.
The Impact of Regulatory Changes on Fintech Innovation
Fintech innovation is shaped at every turn by regulatory forces. We’ve seen these forces accelerate, but also slow the pace of the industry.
This is one reason the RegTech market keeps expanding. Research firms put it at roughly $22 billion to $29 billion in 2026, and The Business Research Company projects about $38.44 billion by 2030 (a 15% CAGR).
How New Regulations Shape Fintech Solutions
Each time a regulator introduces a new requirement, say, around data privacy or digital identity verification, fintech firms must adjust.
Sometimes that means just tweaking a couple of back-end processes; but other times, it requires redesigning entire systems to remain compliant.
A data privacy law, for example, could force a payments app to rethink how it stores transaction histories or manages user consent.
If you have a massive compliance team, you may find these adjustments irritating but manageable. For startups, though, the same changes can feel overwhelming.
The Balance Between Compliance and Innovation
Overly strict requirements implemented by regulatory bodies can slow down the rollout of promising services. But the opposite extreme, too little oversight and financial regulation, can create systemic risks.
The industry hinges on user trust, so the last thing you want is an increase in fraud, consumer exploitation, and unstable markets.
Some regulators have tried to strike a middle ground with regulatory sandboxes and innovation hubs, so companies in the financial services industry can test products in a controlled environment.
However, we constantly notice that what works in a sandbox doesn’t always translate to the complex realities of the global financial industry.
It is still a useful tool, though, and the firms that treat regulatory concerns as a design constraint, rather than a blocker, often produce safer, more scalable solutions, and in some cases, even turn compliance features into market differentiators.
Case Studies of Regulatory Impact on Fintech Companies
The push for stronger anti-money laundering (AML) and know-your-customer (KYC) rules offers a clear case study.
Digital payment platforms, from international remittance apps to buy-now-pay-later services, have had to invest heavily in verifying user identities and tracking suspicious activity.
These changes add friction to the user experience, but compliance here is non-negotiable.
In 2025, regulators worldwide issued about $3.8 billion in AML, KYC, and sanctions penalties, according to Fenergo, and US regulators alone accounted for roughly $1.7 billion.
While the totals have fallen from $6.6 billion in 2023, many theorize that this could just be because of regulator capacity constraints rather than looser expectations.
Cryptocurrency is another good example.
MiCA has been fully applicable across the EU since December 2024, and the transitional period for existing crypto providers ended on July 1, 2026.
Large institutions, with a lot of legacy infrastructure, are also now racing to integrate their own fintech-like services, creating an opportunity for RegTech firms and related fintech platforms to offer their services and partner with these institutions.
The Role of Regulation in the Fintech Sector
As we’ve already mentioned, the fintech industry hinges on trust. You are dealing with people’s money, so any risks present in the evolving fintech landscape quickly outweigh the rewards.
Regulators often need to step in, not to kill innovation, but to set guardrails that protect consumers and preserve trust in the financial system.
At its best, regulatory action creates a level playing field. It helps prevent money laundering and other abuses, and it reassures everyday customers that new services won’t vanish overnight with their savings.
It’s far from flawless, though.
Since something often has to go wrong, or a new technology needs to be developed before the need for new rules presents itself, you could argue that regulators lag behind technology, reacting only after problems surface.
Unfortunately, this assumption is right. And, in some cases, regulators act too late.
The collapse of Wirecard in 2020 is a good example of what happens when oversight fails to keep pace: billions lost, confidence shaken, and new rules introduced only after the damage was done.
6 Key Effects of Regulatory Changes in Fintech
A few shifts stand out as especially influential for fintech businesses right now:
1. Data privacy and security:
Rules such as GDPR in Europe or CCPA in California mean firms can’t just collect and use customer data freely.
Consent must be explicit, and protections airtight.
For fintech startups, this often means hiring compliance experts earlier than planned or redesigning apps to give users clearer consent options.
Since GDPR’s enforcement in 2018, roughly €7.1 billion in fines have been issued, including about €1.2 billion in 2025 alone, a figure that shows regulators aren’t hesitating to punish non-compliance.
2. AML and KYC requirements:
Regulators demand stronger checks to ensure platforms that provide fintech services aren’t unwittingly processing funds tied to crime or terrorism.
That has pushed even small players to adopt sophisticated identity verification tools.
We have helped countless fintech firms integrate and use some form of automated KYC solution to help them comply with regulations.
3. Cryptocurrency oversight:
Whether it’s the SEC in the U.S. or the MiCA framework in the EU, rules are reshaping how exchanges and wallet providers operate.
Business models that thrived in loose environments may no longer be viable.
The collapse of FTX in 2022 accelerated this trend, convincing regulators worldwide that crypto oversight could no longer be optional.
In the US, the biggest change is the GENIUS Act, signed in July 2025, which created the first federal framework for payment stablecoins.
As of September 2026, the OCC, FDIC, Treasury, and other agencies have proposed implementing rules but have not finalized them, and the law takes effect no later than January 18, 2027.
A broader crypto market-structure bill, the CLARITY Act, is less certain. It failed a key Senate procedural vote on September 15, 2026, so stablecoins now have federal rules while much of the rest of crypto market structure does not.
4. Access to payment systems:
For years, most non-bank fintechs have had to reach the Federal Reserve’s payment rails through partner banks. In May 2026, the Federal Reserve proposed a limited “payment account,” often called a “skinny” master account, that would let eligible institutions clear and settle their own payments with a faster approval process than today’s.
The Fed has said it expects to finalize the framework before the end of 2026, but it’s important to keep in mind that the proposal does not change who is legally eligible, and community banks have pushed back on it, so the details may change.
5. AI governance:
AI is now inside credit, fraud, and identity workflows, and regulators are catching up. In the EU, the AI Act treats AI used to evaluate the creditworthiness of individuals as high-risk, which brings requirements for documentation, human oversight, and bias testing.
While the high-risk deadline was pushed from August 2026 to December 2, 2027, the transparency duties already apply, so the delay is a runway rather than a pause.
In the US, existing fair-lending and consumer-protection rules already apply to AI-driven decisions, so explainability matters either way.
5. Open banking:
Surprisingly, open banking initiatives aim to encourage competition by forcing banks to share data (securely) with third-party providers.
For fintech firms, it’s a mixed blessing, since there are more opportunities for collaboration, but also higher expectations for compliance and security.
In the EU, PSD3 and the Payment Services Regulation (PSR) are set to replace PSD2 and tighten open banking and fraud-liability rules, with most of these changes expected to apply in late 2027 to 2028.
In the US, the CFPB finalized its Section 1033 open banking rule in October 2024, but a federal court has blocked the CFPB from enforcing it while the agency rewrites it, so the first compliance deadline, originally set for April 2026, never became binding.
Even so, consumer-permissioned data sharing is not going away, so your teams will probably be better off designing for consent and security now than waiting for the final text.
For leaders, the challenge is interpreting any new rules and operationalizing them in real time.
Regulatory Compliance Challenges for Fintech Businesses
Large financial institutions may have teams of lawyers to untangle new regulations, but a small fintech startup might only have a part-time compliance officer, creating an imbalance in markets.
However, older institutions often struggle with extensive legacy systems, and they struggle to retrofit decades-old infrastructure to meet today’s expectations.
Our recommendation in both these instances is, instead of spending an arm and a leg on developing the systems that facilitate KYC and AML onboarding checks, consider hiring nearshore or offshore developers who have worked with U.S. companies in similar situations and understand the complex regulatory landscape.
Global Perspectives on Fintech Regulation
A few big themes are shaping the future across borders:
- Cross-border cooperation: Regulators are increasingly aware that financial services don’t respect national boundaries. Expect more attempts to harmonize standards, even if perfect alignment remains elusive.
- Operational resilience and AI governance: The EU’s DORA (in force since January 2025) sets hard requirements for operational resilience and third-party risk, and the EU AI Act is phasing in obligations for high-risk AI such as credit scoring, with those deadlines now set for December 2027.
Preparing for Regulatory Changes in the Fintech Sector
Since innovation in fintech is only speeding up, staying ahead of regulatory change demands forward-looking strategies and a culture of preparedness.
Strategies for Fintech Companies to Ensure Compliance
As we have already mentioned, the firms that stay ahead usually treat compliance as a living system rather than a set of static checkboxes.
That means building programs with clear policies and controls, but also testing whether those rules actually work in day-to-day operations.
Technology helps.
Automating KYC and AML checks, or streamlining regulatory reporting, cuts down on human error and can save startups from drowning in manual paperwork.
However, even the most advanced compliance software needs people who understand the regulations behind the algorithms.
Fintech companies need regular risk assessments and internal audits, which can help you uncover cracks before regulators or customers do.
There’s also value in dialogue. Too many companies view regulators as adversaries when, in reality, seeking guidance early can prevent expensive missteps later.
Proactive engagement not only reduces uncertainty but also signals credibility.
What Regulatory Changes Mean for Your Engineering Team
Every new rule eventually lands in a backlog, and someone has to build it. Looking across the changes above, the engineering work tends to fall into a few buckets:
- Consent and data access: Consent capture, revocation, and data-sharing APIs, driven by GDPR, PSD3, and the PSR, and eventually CFPB Section 1033.
- Auditability: Logs, evidence trails, and reporting that show a regulator what your system did and why, from AML case files to DORA incident reports.
- Vendor and partner risk: Registers of third-party providers, contractual controls, and due diligence, whether the pressure comes from DORA or from your sponsor bank.
- Jurisdiction-aware rules: Licensing status, product availability, and disclosures that vary by US state or country. These are much easier to change as configuration than as hard-coded logic.
- Model governance: Documentation, explainability, and bias testing for credit and risk models, especially under the EU AI Act.
Conclusion
Compliance, when treated as an afterthought, is expensive and limiting. But compliance, when treated as a design principle, can actually clear the way for sustainable growth.
You see it in startups that bake KYC checks directly into their onboarding flows, or in payment apps that treat privacy features not as a burden but as a selling point. These companies aren’t just following the rules; they’re using the rules to build trust.
At Trio, we’ve seen this play out across fintech teams of every size. Our work often begins with founders or executives who feel boxed in by compliance, and ends with them realizing that it can be the very thing that makes their product scalable, secure, and market-ready.
If you need fintech specialist developers on your team or want to know more about how you can approach regulatory challenges and compliance in your company’s tech, reach out to us.