

 Read Client Stories




 Alex Kugell
 Key Takeaways
- Generic distributed-team advice covers coordination. Fintech nearshore collaboration needs to cover compliance, too, because, in a regulated environment, the collaboration process itself forms part of the control environment.
- Code review functions as a SOC 2 and PCI DSS change-management control in fintech. The pull request approval record becomes audit evidence.
- LATAM timezone overlap (4-8 hours with US teams, near-full-day from Colombia) should be protected for compliance decisions and complex collaboration.
- Compliance questions block engineering progress. Every hour a compliance question sits unanswered in a queue costs more than just that hour. Same-day resolution is the standard to target.
- A nearshore engineer needs scoped access, synthetic data environments, and compliance context provided before day one.
- Activity metrics (commits, lines of code, hours logged) tell you motion. Cycle time, sprint predictability, and compliance-decision latency tell you whether the collaboration process actually works.
For a fintech team, a well-run nearshore engagement can be incredibly beneficial, but a problematic one can lead to massive tech debt and also open you up to regulatory issues.
General recommendations to ensure a successful collaboration apply, but there are some unique considerations that apply only to fintech.
The collaboration process forms part of the compliance posture.
Let’s look at how to layer the fintech compliance requirements onto the standard distributed-team foundation, including the tooling stack and its security overlay, the sync/async cadence that LATAM timezone overlap makes practical, fintech-specific collaboration practices, onboarding structure for regulated environments, and the metrics worth tracking.
At Trio, we specialize in fintech, providing companies with developers from regions like LATAM who have production experience in similar products, and working with US companies remotely.
The Tooling Stack (with the Fintech Security Overlay)
A nearshore fintech team needs the same categories of tools as any distributed team, but these tools need to be configured with access controls and audit requirements.
| Category | Common tools | Fintech configuration note |
| Instant messaging | Slack, Microsoft Teams | SSO-enforced. Sensitive data stays out of channels, with a dedicated channel for incident response. |
| Video/sync | Zoom, Google Meet | Architecture and compliance decisions are recorded and stored as documentation. |
| Project management | Jira, Linear | Tickets reference compliance requirements where relevant, producing a full audit trail of work history. |
| Documentation | Confluence, Notion | The system of record for architectural decisions and compliance reasoning. |
| Version control | GitHub, GitLab | Branch protection rules enforced, mandatory review before merges, and signed commits where required. |
| Design | Figma | Scoped access with no production data or PII in mockups. |
| Secrets/access | Okta/SSO, VPN, IAM | Least-privilege access so that nearshore engineers access only what their role requires. |
Four overlays distinguish a fintech-configured stack from a standard one:
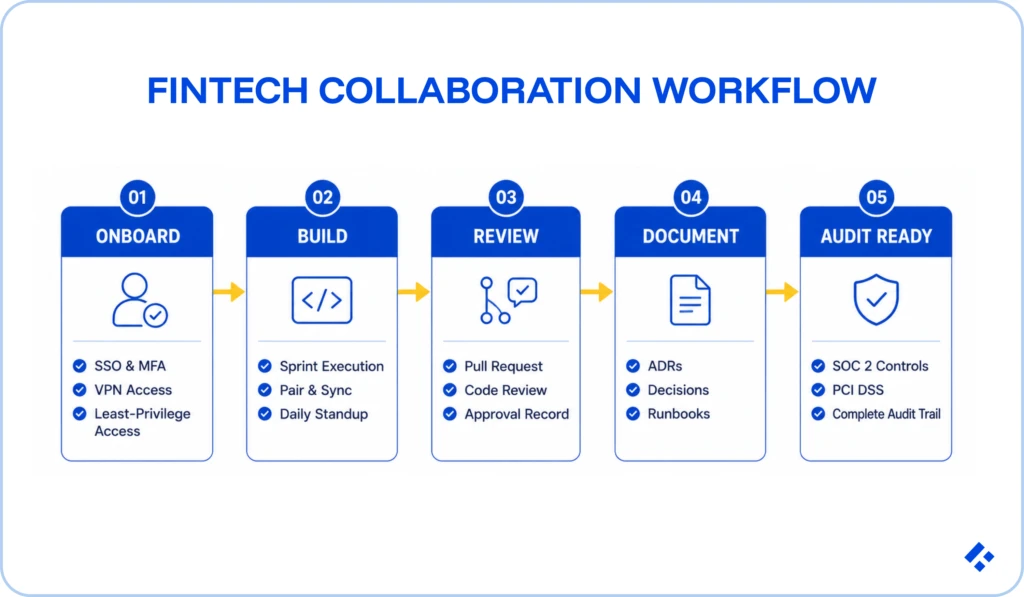
- Single sign-on across all systems: Every tool a nearshore engineer touches should sit behind SSO with enforced multi-factor authentication. This satisfies SOC 2 access-control expectations and prevents credential-sharing patterns that tend to emerge organically in distributed team setups.
- VPN for sensitive resource access: Production-adjacent systems, internal APIs, and compliance-scoped environments should require VPN. The access audit trail that creates matters as much as the security protection itself.
- Scoped, least-privilege access: An engineer working on a non-PCI feature doesn’t need cardholder data environment access. Provisioning should match the role and expand only when required.
- Tool parity: The nearshore engineer uses the same tools, in the same configuration, as the internal team. Parallel stacks, where a nearshore team operates separately, produce the audit-trail gaps and security exceptions that compliance reviews tend to surface.
The Sync/Async Cadence: What LATAM Overlap Makes Possible
LATAM engineers share 4-8 working hours with US teams, depending on the specific country.
Colombia, for example, shares nearly a full US Eastern business day, making real-time collaboration very practical. Allocating overlap time deliberately rather than letting it fill with whatever surfaces first is incredibly important.
Use the overlap window for:
- A single shared daily standup for all developers, where the nearshore engineer reports into the same call as the internal team.
- Architecture and compliance decisions. A PCI DSS scope question resolved in a 20-minute synchronous discussion saves the 24-48-hour cycle of overnight queues.
- Pair programming on compliance-sensitive code. Real-time pairing on payment idempotency logic or ledger reconciliation catches issues before they enter the review queue.
- All agile ceremonies, like sprint planning, review, and retrospective.
- Incident response. Payment failures and reconciliation discrepancies need real-time collaboration.
Push to async:
- Status updates can be written in the project tool.
- Routine code review handoffs (compliance-sensitive reviews still benefit from a synchronous walkthrough).
- Documentation.
- Routine progress reporting.
Five Fintech-Specific Collaboration Practices
Each of these five practices addresses a place where the collaboration process directly intersects with compliance controls.
Practice 1: A Fast Escalation Path for Compliance Decisions
Compliance questions block engineering progress.
If your engineer isn’t sure whether a logging statement captures card data or whether a KYC flow needs an additional state, they can’t proceed safely without an answer. Guessing should always be discouraged as it creates compliance risk that may not surface until an audit.
In a distributed team, that question may sit for 24-48 hours if you try to handle it asynchronously.
The engineer context-switches and re-engages after the answer takes more time. Multiply that across a sprint, and the overhead adds up.
The easy solution here is to have a named person or dedicated channel responsible for compliance decisions, committed to resolving compliance-blocking questions within the overlap window.
This encourages these issues to be resolved in the same business day, allowing your projects to stay on track.
The rule: no compliance question waits in a backlog.
Practice 2: Code Review as a Change-Management Control
Code review on a fintech team serves two functions at the same time: it’s a quality practice and SOC 2 and PCI DSS change-management control. Your collaboration process needs to treat it as both.
- Mandatory review via branch protection: No code reaches production without a documented, approved review. Branch protection rules enforce this at the version control level, not as a team convention that might lapse under deadline pressure.
- Documented approval as audit evidence: The pull request record, who reviewed, what got approved, and when the approval landed, becomes compliance evidence. The review process should produce this record automatically.
- Synchronous walkthrough for compliance-sensitive changes: Payment logic, KYC flows, and ledger code benefit from a synchronous review walkthrough during the overlap window. An async review can miss context.
Practice 3: Least-Privilege Access Management
How a nearshore engineer accesses systems is governed by least-privilege requirements under SOC 2 and PCI DSS. The goal should be to collaborate as productively as possible within those requirements.
Engineers should only get access to the relevant repositories and environments, not to the cardholder data environment.
You should also develop and test against synthetic data reflecting production distributions without exposing real PII.
Finally, VPN connections and IAM authentication events should produce the access audit trail that SOC 2 and PCI DSS require automatically.
Practice 4: Audit-Ready Documentation
Documentation in a regulated environment serves two purposes at once: knowledge-sharing within the team and audit evidence that needs to survive beyond any individual’s tenure on the engagement.
It is essential that you make documentation a deliberate practice:
- Document architectural decisions with their compliance reasoning: Why the KYC state machine has these states, why the idempotency key gets generated client-side, or how the PCI DSS scope boundary was drawn. An auditor asks for this reasoning.
- Decision records over code comments: Architectural Decision Records (ADRs) or their equivalent capture reasoning in the documentation system. We recommend Confluence or Notion, where it persists independently of codebase versions and stays accessible to compliance teams and auditors.
- Documentation as a definition-of-done criterion: A compliance-touching story is only done when the feature works and its decision reasoning gets documented.
This practice also protects institutional knowledge inside the team, which is one of the primary structural advantages of the embedded staff augmentation model over project outsourcing, where knowledge walks out when the contract ends.
Practice 5: Compliance-Aware Sprint Cadence
Security reviews, compliance validation, audit evidence preparation, and documentation of compliance-touching changes all need real engineering time. That time needs to be planned explicitly.
In our experience, fintech engineering teams consistently find that compliance work consumes a meaningful share of each sprint, and if they don’t account for it early, they discover the overhead mid-sprint, when compliance activities compete with feature delivery and predictability drops.
To avoid this, make sure to surface compliance blockers in planning. Identify which stories touch the compliance perimeter and what compliance work, review, documentation, and validation they require.
And, as we mentioned above, ensure that compliance belongs in the definition of done. For example, a story touching payments, KYC, or the ledger is only complete when the feature works, passes review as a control, gets documented for audit, and clears compliance validation.
Related Reading: Fintech Hiring Slowdown
Onboarding a Nearshore Fintech Engineer
The first two weeks of onboarding usually determine whether a nearshore engineer becomes a productive team member or a perpetual outsider.
Remember that fintech onboarding carries a compliance dimension that is unique to the industry.
Week 1: access, context, and compliance grounding
Provision scoped access before day one, making sure that you get all accounts, repositories, environments, SSO, and VPNs. We recommend that you run off a documented pre-boarding checklist so you avoid missing anything and wasting time.
Also, make sure that you provide the product and compliance context early.
Cover what the product does, which regulatory frameworks apply (PCI DSS, KYC/AML, SOC 2, others), and why key architectural decisions were made.
This lets them make compliance-aware decisions independently.
It is also helpful to walk the developer through the tools and the processes you use. Cover the code review control, the documentation practice, the escalation path, the sprint cadence, and the definition of done.
Week 2: integration and first contribution
Include the engineer in all ceremonies from day one. Standups, planning, and retrospectives should be attended as if they were part of your internal team.
Pair them with an internal engineer on their first compliance-touching task. The review-as-control and documentation practices land differently when demonstrated in a real pull request, and you can rest easy knowing that the risk of compliance issues will be minimized.
Finally, we always see great results when people invest in cultural integration. Virtual coffee chats, introductions, and inclusion in non-work channels help the embedded engineer who feels part of the team contribute like part of the team.
The Metrics That Matter
It is important to measure outcomes, but be careful to avoid the trap of measuring activity.
For a nearshore fintech team, the metrics worth tracking combine standard delivery signals with a compliance-quality dimension.
Delivery metrics:
- Cycle time, from ticket start to production deployment. Rising cycle time often signals decision latency, or compliance questions queuing overnight.
- Sprint predictability, planned versus delivered, with compliance capacity accounted for. Consistent under-delivery almost always means compliance overhead isn’t getting planned in.
- Pull request review time. In fintech, where review functions as a change-management control, slow review delays the whole pipeline and creates audit gaps.
- Compliance-blocking decision latency. How long do compliance questions wait for an answer? They should be addressed on the same day.
Compliance-quality metrics:
- Documentation completeness. Are compliance-touching changes documented at sprint close? Make sure to measure this at the sprint review.
- Production defect rate in compliance-sensitive code. Specifically look at payment, ledger, and KYC defects reaching production. The ultimate quality signal in a fintech context.
Metrics like hours logged, commit counts, and lines of code all measure motion rather than value, and in a distributed team, they reliably incentivise the wrong behaviour, so we recommend that you avoid them.
Running a Nearshore Fintech Team with Trio
At Trio, we place pre-vetted fintech engineers from LATAM into US and EU fintech teams as embedded, dedicated collaborators through staff augmentation.
Our engineers join your team. They’re in your standup, your code review control, your documentation system, and your escalation path.
The vetting process confirms fintech domain competency, so you can rest easy knowing that the engineer arrives with compliance context already in place rather than learning it on your codebase.
We also handle the employment structure, access compliance documentation, and engagement governance that a regulated environment requires.