

 Read Client Stories




 Alex Kugell
 Key Takeaways
- The core difference from general web development is architectural. A fintech web app needs to handle real-time financial data, regulatory compliance, and security requirements that a typical business web app never encounters.
- API-first architecture has become the default starting point for fintech products in 2026.
- AI adoption has moved from differentiator to baseline, and that expectation increasingly shows up in RFPs whether or not it’s explicitly requested.
- Zero-trust security, verifying every request regardless of where it originates, is the expected baseline for a serious fintech platform now.
- Whether to build browser-based, native mobile, or both depends on your actual users.
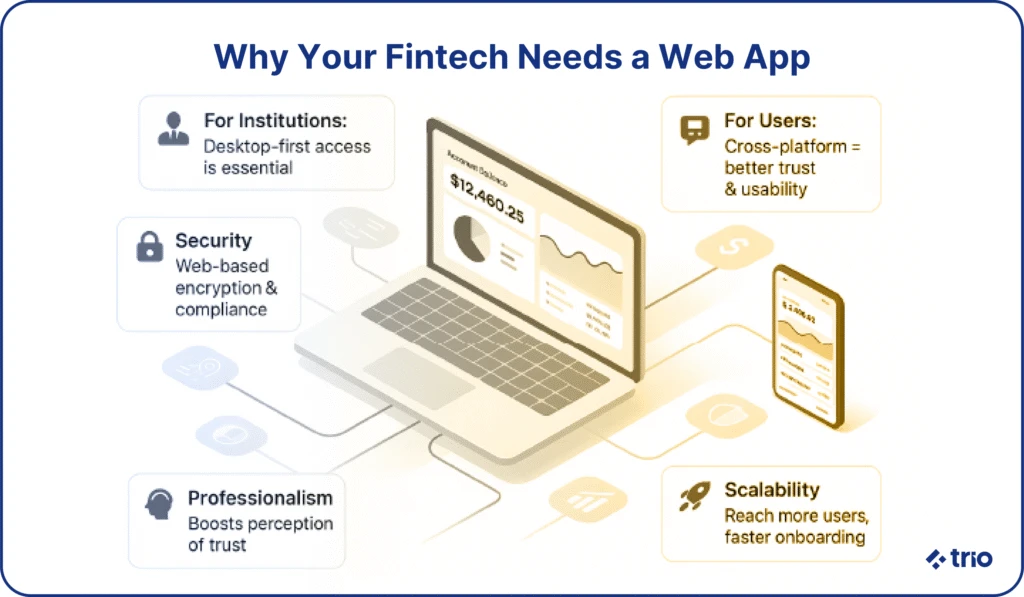
While users definitely find value in mobile apps, there is a time and place for web apps. Some services work better on larger screens, like investment apps and enterprise internal tooling.
However, you are still subject to regulations and user expectations that differ from generic web apps, and you need to understand that industry nuance before you start developing, so you can not only plan sufficiently, but also hire the right people.
Let’s look at everything to understand what actually makes a fintech web app different from any other web app before you even get to that conversation.
If you need senior fintech developers with production experience creating successful web apps in the industry and dealing with edge cases, we can assist.
What Makes Fintech Web Development Different
A fintech web application is a browser-based tool that handles financial services. Some examples our developers have built include banking dashboards, payment platforms, investment tools, and lending products.
All of this is built on the same core web technologies as any other web app, but these tools are shaped by requirements that don’t show up anywhere else in typical business software.
The users could be individuals, SMEs, or institutions. Depending on who you are targeting, you may have to deal with incredibly varied transaction volumes, compliance scopes, and how much the interface needs to prioritize real-time accuracy over general usability.
You’ll also need to decide early whether the product you are thinking of creating benefits from being browser-based specifically.
Since most of the general public finds mobile applications more convenient, we have found that mobile-native development often makes more sense outside of enterprise environments.
The Compliance Layer Most Web Apps Never Touch
The fintech market is heavily regulated. Whether you’re building a mobile banking dashboard or a browser-based crypto wallet, you’re almost certainly going to need to comply with data protection regulations that vary meaningfully by region.
That needs to be factored into your architectural decisions from the start.
Regulations are consistently a large part of why fintech founders that we have worked with end up underestimating cost.
Make sure that you account for compliance controls, audit-ready logging, and security architecture built to survive real regulatory scrutiny.
This is also the practical reason so many fintech startups, scaleups, and enterprises outsource this specific portion of development rather than building it entirely in-house.
A partner who’s built compliant fintech products before has already made the mistakes that cost a first-time team months, and can prevent you from doing the same.
API-First Architecture Is the 2026 Default
Successful fintech teams increasingly design the API before the interface.
API-first means every capability (onboarding, KYC, payments, and reporting) gets designed as an API first, with the web interface built as one consumer of that API rather than the other way around.
This matters practically because it’s what lets a fintech platform scale individual services without touching the rest of the system.
It is also what makes integrating a new partner or launching a new product later a configuration change rather than a rebuild.
A central API gateway handling authentication, rate limiting, and routing is standard now, and a growing number of teams that we have worked with use a Backend-for-Frontend pattern specifically: tailored APIs for mobile versus web clients.
Since this is such a pivotal part of the architecture, security is critical. The gateway itself functions as a compliance boundary, so every request that flows through it is a potential audit event.
Financial-grade API security patterns (strict authentication proofing, request signing, mutual TLS) are becoming the expected baseline for serious fintech platforms.
Real-Time Data Changes the Engineering Problem
A fintech web app usually can’t get away with the eventual-consistency patterns a typical business dashboard would otherwise tolerate just fine.
A balance that’s a few minutes old, or a trade confirmation that arrives late, quickly creates a trust problem.
That needs to be accounted for in your architectural decisions.
Think about things like where to use genuine real-time updates versus polling, how to make staleness visible to the user rather than hiding it behind a confident-looking number, and how to keep the interface itself performant when the underlying data is changing constantly.
What the Architecture Actually Looks Like
We have already discussed the API layer.
Outside of that, a fintech web app tends to converge on a similar set of services regardless of the specific product, including:
- An API gateway as the single entry point handling routing and rate limiting.
- A dedicated auth and identity service supporting OAuth2/OpenID Connect with multi-factor authentication.
- Separate payment and ledger services that keep money-movement logic isolated from the rest of the application.
- An asynchronous KYC/AML engine for identity verification and risk scoring.
- An event bus (commonly Kafka or a managed equivalent) to guarantee ordered, durable delivery for anything touching reconciliation.
On the data side, a transactional database built for integrity (PostgreSQL is the common default, sometimes paired with a distributed option like CockroachDB for global scale) sits alongside dedicated observability tooling.
This is because knowing a payment failed matters less than knowing exactly when, where, and why it failed.
Cost is worth being realistic about too.
A conservative fintech MVP, core account creation, light KYC, basic payments, and reporting can start at as little as $50,000, and move all the way into the $150,000 range depending on region and compliance scope.
Full-featured platforms regularly start exceeding $200,000 once real integrations and audit-ready infrastructure are factored in.
Security Architecture Regulators Actually Expect
Zero-trust security, where you verify every request regardless of whether it originates inside or outside your own network, is the approach most are taking.
Any of the breaches in financial services involve compromised credentials or weak authentication specifically, which is a strong argument for treating identity and access as the priority.
Production systems handling real financial data increasingly need resilience designed from day one, too.
Think about things like defined recovery objectives, multi-region redundancy for anything mission-critical, and disaster recovery capability that regulators are increasingly asking teams to actually document, not just claim.
AI has become part of this picture as well, and shows up most concretely in fraud detection and credit decisioning.
The new architectural issue this has created is: when an AI agent is initiating actions on a user’s behalf, does your API design assume a human is always the one making the request?
Choosing How to Build It
In many cases, successful fintech startups, scaleups, and enterprises outsource this portion of development to a software development company rather than building the full compliance and security layer in-house from scratch.
There are many reasons why you may want to do this, including the reduced time to find the right talent and the guaranteed production experience. If you approach nearshore and offshore partners, you also widen your candidate pool.
At Trio, we provide experienced developers through nearshore and offshore staffing models specifically because of fintech-specific judgment.
Knowing which parts of a system need extra caution and which don’t is genuinely hard to build quickly on a first attempt, and expensive to learn the hard way in production.
To find out more about whether we have the right skillset for you, request a consult.